De shop is live

Wij bouwen Workstation AI-machines voor websites, AI-agents en LLM-training — configureer en koop online.

Bekijk handelsprijzen
AI-producten
AI LabsOpenAI-agentsClaude-agentsGrok-botWorkstation AI native CRMMarketingAlle producten
AI-oplossingen
Toegepaste AIAI-agentsGeneratieve AIAI-automatiseringAI-bijscholingAI-pakketten voor het mkbEnterprise AI LabAI-werkstationsNVIDIA-hardware en -softwareNVIDIA Accelerated ComputingPrivate AIGPU private cloudGPU-clustersEdge AIAI per sector
AI-diensten
PlatformmoderniseringDigitale engineeringDatafundamenten en AIAutonome operatiesAI-adviesDevOps-automatiseringCybersecuritySoftwareontwikkelingAgentontwikkelingMLOps-opzetGPU-leasingGPU private cloud
Over ons
BedrijfOns verhaalPartnersKlantverhalen
AI-datacenters
AI-datacentersGPU private cloudGPU-clustersGPU-leasing
AI-inzichtenJev-reeksBenchmarklabModelkeuze
Technische notities
Documentatie
Linux-OSUbuntuRed Hat Enterprise LinuxSUSE LinuxAlpine LinuxDebian, Rocky & AlmaLinux
AI-cloudplatformsAWS & Amazon BedrockGoogle Cloud & Vertex AIMicrosoft Azure & AI FoundryGPU-clouds en -marktplaatsen
Private AI-datacentersVoor advocatenkantorenVoor accountantskantorenOn-premises platformsVolledig beveiligde cloud
ToolsRing PromoterJobshout
Nieuws
Blog
Neem contact opInloggen

AI-werkstations, AI multi-agent software, GPU-infrastructuur en intelligente agentoplossingen voor moderne bedrijven.

Neem contact op

AI-oplossingen

Toegepaste AIAI-agentsGeneratieve AIAI-automatiseringAI-bijscholingAI-pakketten voor het mkbEnterprise AI LabAI per sector

Producten

Alle productenWorkstation AI-native CRM & ERPMarketingOpenAI-agentsRing PromoterJobshout

Bedrijf

Over onsBedrijfAI-datacentersWaarom WorkstationPartnersKlantverhalenPrijzenContactTenthMatrix

Bronnen

AI-inzichtenTechnische notitiesDocumentatieLinux-OSAI-cloudplatformsPrivate AI-datacentersBlogZoekenSitemap
Kantoor België
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683Ma - Vr: 9:00 - 18:00 CET
+32 492 45 67 46
Hoofdkantoor VK
77-79 Marlowes, Hemel Hempstead HP1 1LFRoute: neem afrit 20 van de M25, Outer LondonBedrijfsnummer: 11641870Ma - Vr: 9:00 - 18:00 GMT
+44 7515 356 146
Kantoor India
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841
Kantoor Taiwan
3F, No. 2-4, Aisi Rd., Ren'ai Dist., Keelung City 200, Taiwan基隆市仁愛區愛四路2之4號3樓Ma - Vr: 9:00 - 18:00 Taiwanese tijd (GMT+8)
+886 926 892 701+32 492 45 67 46
Kantoor Estland
Aleksander Puškini tn 30-25, 20306 Narva, EstoniaMa - vr: 9:00 - 18:00 uur Estse tijd (EET)
+32 492 45 67 46

© 2026 Workstation AI. Alle rechten voorbehouden.

PrivacyGegevensverwijderingCookiesServicevoorwaardenWebsite-sitemap

NVIDIA, het NVIDIA-logo, RTX, RTX PRO, Blackwell, CUDA, NVLink, MGX, Omniverse, Spectrum-X, Quantum, BlueField, DGX en HGX zijn handelsmerken en/of gedeponeerde handelsmerken van NVIDIA Corporation in de VS en andere landen. AMD, het AMD Arrow-logo, EPYC, Instinct, Ryzen en Threadripper zijn handelsmerken van Advanced Micro Devices, Inc. Dell en PowerEdge zijn handelsmerken van Dell Inc. of haar dochterondernemingen. Intel en Xeon zijn handelsmerken van Intel Corporation of haar dochterondernemingen. AMAX, AceleMax en LiquidMax zijn handelsmerken van AMAX Engineering Corporation. Alle andere productnamen, logo's en merken zijn eigendom van hun respectieve eigenaren. Wij gebruiken ze uitsluitend om de producten aan te duiden die wij beschrijven, leveren of ondersteunen; het gebruik ervan betekent niet dat de eigenaren ons onderschrijven.

Home / Technische notities / Technology
DevOpsSecuritySREKubernetes

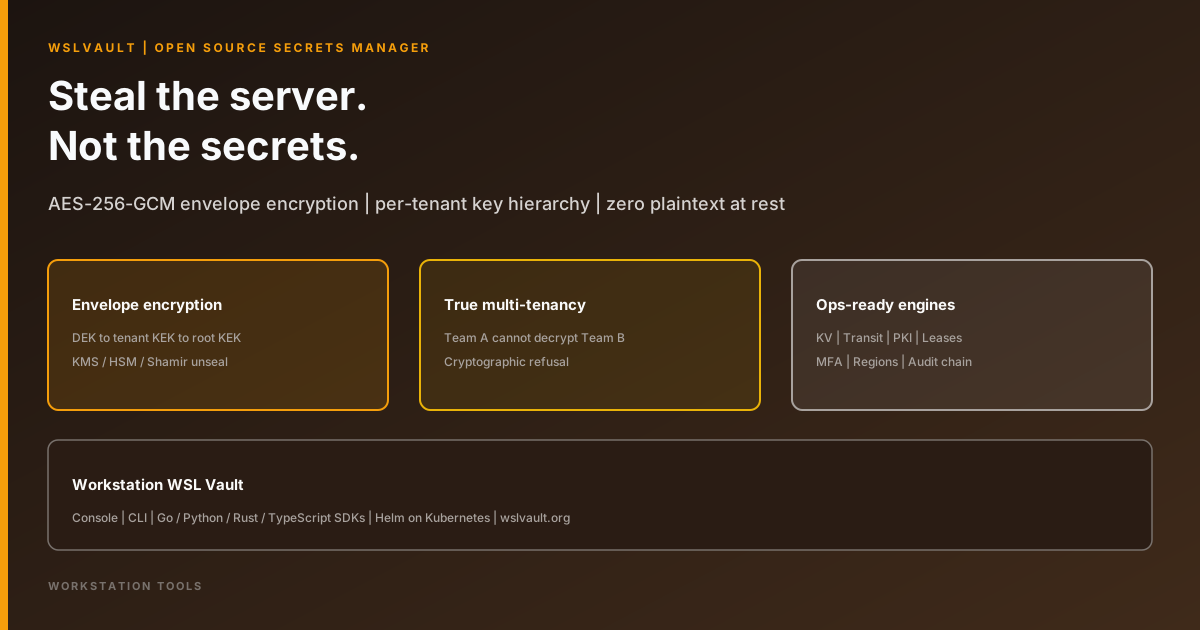
WSLVault: Steal the Server. Not the Secrets.

Technical brief: AES-256-GCM envelope hierarchy, cryptographic tenant isolation, engines, identity/MFA, active/active regions, Kubernetes deploy, and video chapters

22 september 2026Technology3 min read

This is the long-form deep dive companion to the intro blog. Product page: Workstation WSL Vault · wslvault.org · GitHub.
WSLVault — steal the server, not the secrets

20-minute intro — youtu.be/O6q3_H0k2M8

Thesis. Secrets management fails closed only when ciphertext at rest is worthless without key custody. WSLVault wraps every secret under a per-tenant hierarchy (DEK → tenant KEK → root KEK) so a stolen server, disk, or database dump does not equal stolen secrets.

1. Why this matters — steal the server

Classic failure mode: back up a database, lose a laptop, or compromise a host — and the attacker leaves with readable credentials. “Encryption at rest” that shares one key across every tenant, or that stores unwrapped material beside ciphertext, collapses under that scenario.

WSLVault’s design answer is simple to state and hard to fake: seal secrets before they touch disk, isolate tenants at the key layer, and keep root custody outside the data plane (KMS, HSM, or Shamir quorum).

2. What WSLVault is

WSLVault is an open-source, self-hosted secrets manager with Vault-compatible workflows:

  • Versioned KV secrets
  • Transit encryption (encrypt / decrypt / sign / verify)
  • PKI and short-lived certificates
  • Dynamic leases with real revoke
  • Identity, policies, and MFA
  • Active/active multi-region replication
  • Tamper-evident, hash-chained audit

Operators drive it from a web console, CLI, Go/Python/Rust/TypeScript SDKs, or MCP. Deploy with Helm/GitOps on Kubernetes. Product home: https://www.wslvault.org/.

3. Envelope encryption and key hierarchy
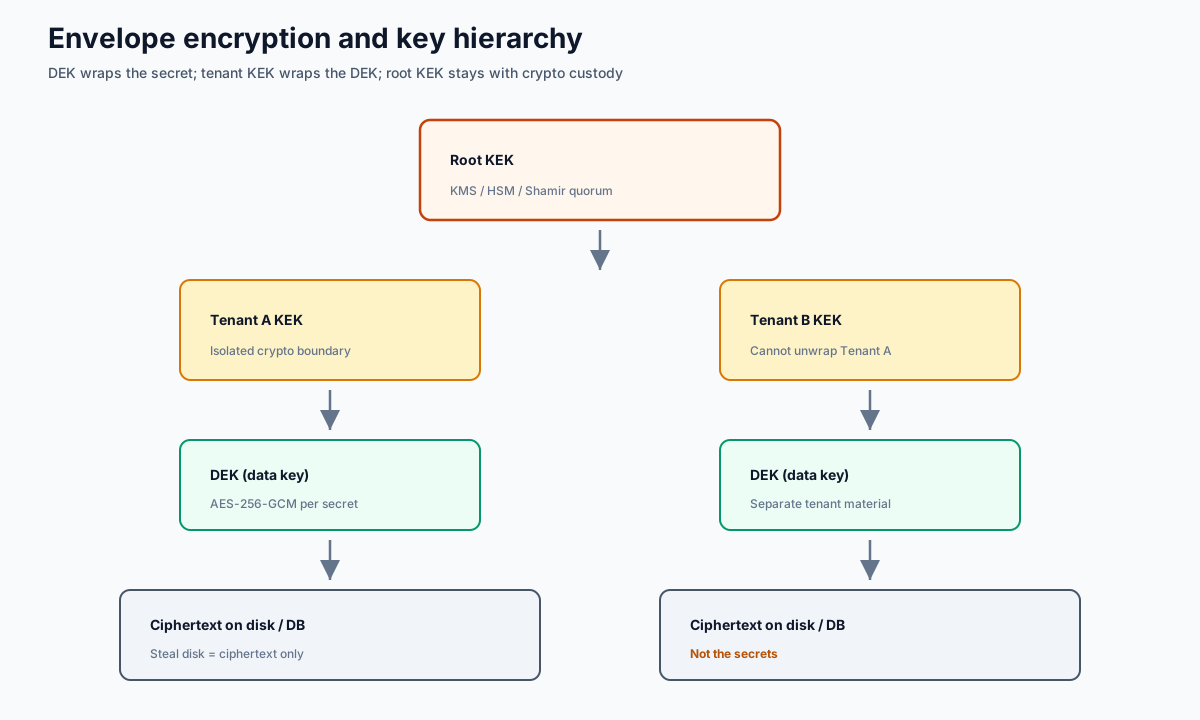
WSLVault envelope encryption hierarchy

Each secret is sealed with a data encryption key (DEK). The DEK is wrapped under a tenant KEK. Tenant KEKs are wrapped under a root KEK held by the crypto service — typically backed by KMS, HSM, or Shamir-split custody so no single operator can unseal alone.

AES-256-GCM provides authenticated encryption. A database dump yields ciphertext wrapped under keys the database never sees. That is the practical meaning of steal the server, not the secrets.

4. Multi-tenancy that actually isolates

Application “tenant IDs” are not enough. In WSLVault, a data key belongs to exactly one tenant. A cross-tenant request returns “not found” rather than another tenant’s data. Isolation holds at the crypto service — Team A cannot decrypt Team B even if a bug in an upper layer misroutes an identifier.

That is cryptographic refusal, not an “oops” in a filter.

5. Console surfaces: secrets, transit, PKI

The steel/brass console walks the same engines as the API:

Engine What operators get
KV v2Versioned reads/writes, check-and-set, soft-delete/destroy, per-path metadata — sealed before storage
TransitEncrypt/decrypt/sign/verify without plaintext keys leaving the vault; rotate while old ciphertext stays readable
PKIPrivate CA, roles, short-lived certs; CA private keys envelope-encrypted under their own root

6. Identity, policies, leases, and MFA

Identity comes from a signed, per-tenant token — never a trusted header alone. Operators get self-service TOTP two-factor with recovery codes, fine-grained policies on API keys and JWTs, plus SCIM, LDAP, OIDC, mTLS, and cloud-workload auth patterns.

Dynamic credentials are leases: issued, listed, renewed, and revoked for real. Revoking a token stops it working immediately — not just flipping a row that something might ignore.

7. Regions, HA, and audit
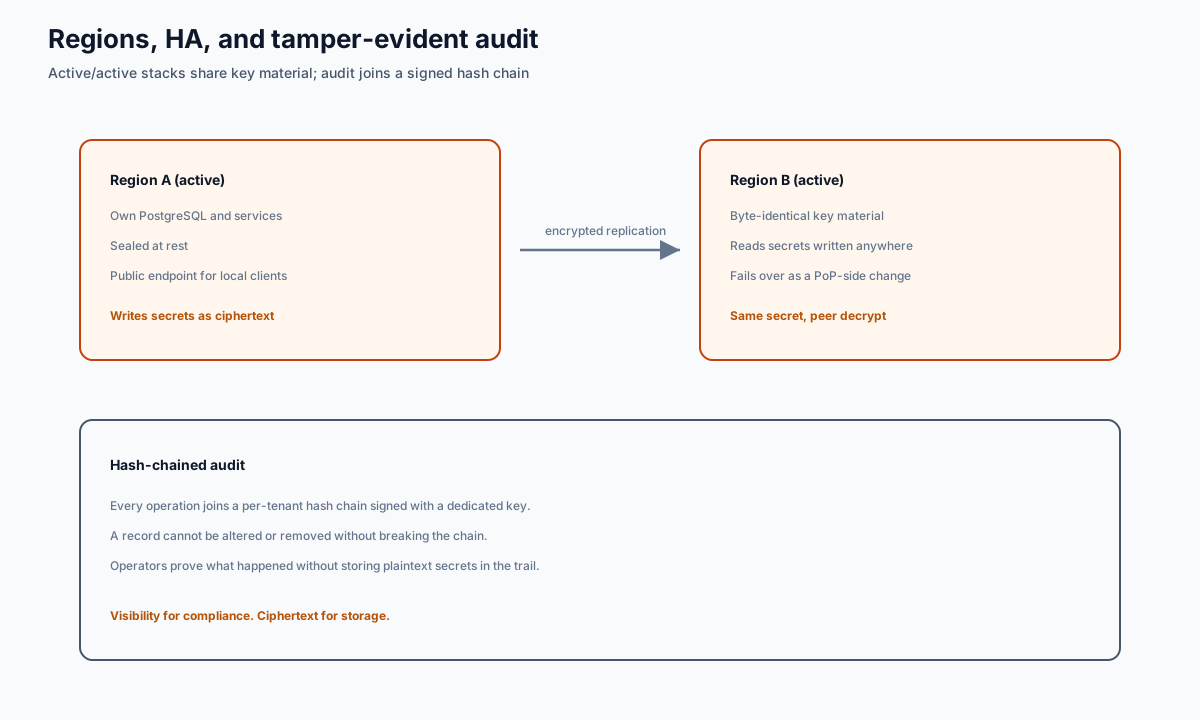
WSLVault multi-region replication and audit

Each region is a complete stack — its own database, services, and public hostname. Regions share key material, not a single live database. Replication moves encrypted changes so a peer can decrypt what was written elsewhere.

Every operation joins a per-tenant hash chain signed with a dedicated key. A record cannot be altered or removed without breaking the chain. That gives compliance visibility without storing plaintext secrets in the trail.

8. Deploy on Kubernetes

Ship with the Helm chart and Kubernetes operator, drive from GitOps, scrape with Prometheus, and reach the vault from SDKs or an AI agent over the built-in MCP server. Start from the official guide: GETTING-STARTED.md.

9. Video chapters

Time Topic
0:00Why this matters (steal the server)
1:30What WSLVault is
3:00Envelope encryption and key hierarchy
5:30Multi-tenancy that actually isolates
8:00Console walkthrough (secrets, transit, PKI)
11:00Identity, policies, leases and MFA
14:00Regions, HA and audit
17:00Deploy on Kubernetes
19:00Where to go next

10. Where to go next

  • Product: /en/wsl-vault
  • Site: wslvault.org
  • Repo: github.com/bwalia/wslvault
  • Docs: docs/
  • Related Workstation tools: WSL Proxy, Ring Promoter

Published by Workstation.
Deel dit artikel

Meer in Technology

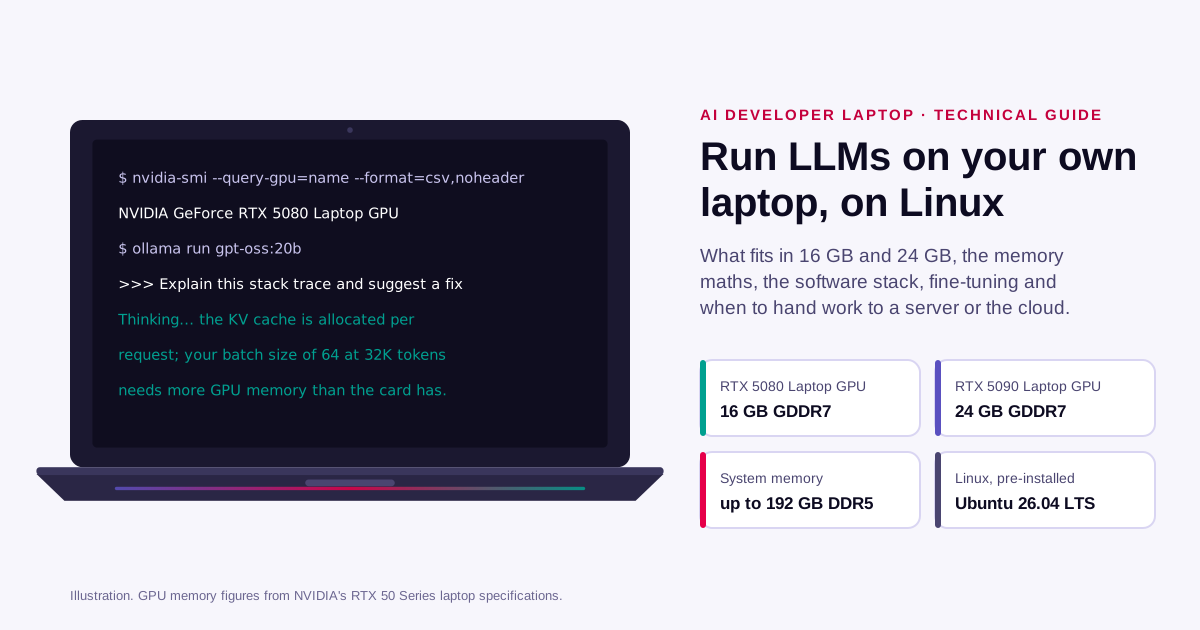
AI-developerlaptops: LLM's lokaal draaien onder Linux met GPU's van 16 GB en 24 GB (gids 2026)

AI-developerlaptops: LLM's lokaal draaien onder Linux met GPU's van 16 GB en 24 GB (gids 2026)

Wat er past op een RTX 5080 of RTX 5090 Laptop GPU, de geheugenberekening, de open modellen die de moeite waard zijn, Ubuntu 26.04 inrichten met de NVIDIA-stack, Ollama, llama.cpp en vLLM, codeerassistenten, LoRA-fine-tuning, beveiliging, en wanneer werk naar een server moet

Lees meer
ML- en LLM-systemen testen die u niet correct kunt bewijzen: een Python-kit voor bewijsmateriaal

ML- en LLM-systemen testen die u niet correct kunt bewijzen: een Python-kit voor bewijsmateriaal

Bewijsmateriaal in plaats van bewijzen, in ongeveer 400 regels Python met echte output: slice-metrics met bootstrap-intervallen en een pass/fail-contract, property- en metamorfe tests met Hypothesis, kalibratie en conformal prediction, Pydantic-contracten en regressie-evals voor LLM-output, driftcontroles, een CI-gate en exacte verificatie van een klein neuraal netwerk

Lees meer
TorchCurves in de praktijk: leerbare B-spline- en Legendre-curves in PyTorch

TorchCurves in de praktijk: leerbare B-spline- en Legendre-curves in PyTorch

torchcurves installeren, een curve fitten en dimensioneren, kiezen tussen B-spline en Legendre en de input map, een monotone kalibratiecurve en een additief model op tabeldata bouwen, vergelijken met SciPy, scikit-learn, een KAN en een MLP, coëfficiënten naar JSON exporteren, testen en in productie draaien, met echte output

Lees meer